CLS
Cybersecurity

Certified Information Systems Auditor CISA

CISA designation is a globally recognized certification for professionals in auditing control, assurance, and security

Total Duration
40 Hours
Level
Beginner
Category
Cybersecurity
Partner
ISACA
About this course

About this course

Prove your expertise in information systems auditing, control and security and be among the most qualified in the industry.

CISA Certification is world-renowned as the standard of achievement for those who audit, control, monitor and assess an organization’s information technology and business systems.

Being CISA certified showcases your audit experience skills and knowledge and demonstrates you are capable of assessing vulnerabilities, report on compliance and institute controls within the enterprise.

Target Audience

IT Auditors who wish to improve their skills in Information Systems Audit and Assurance.
IT Governance & Risk professionals who are responsible for IT governance, enterprise risk management and compliance.
Security professionals who wish to enhance their understanding of security controls, risk, audit, and assurance.
IT managers and professionals who are responsible for IT management, systems, infrastructure, and information security.
professionals who are preparing for the CISA certification exam

Prerequisites

There are no specific entry requirements to participate in this CISA training.

Course Outline

  • IS Audit Standards, Guidelines, Functions, and Codes of Ethics
  • Types of Audits, Assessments, and Reviews
  • Risk-based Audit Planning
  • Types of Controls and Considerations
  • Audit Project Management
  • Audit Testing and Sampling Methodology
  • Audit Evidence Collection Techniques
  • Audit Data Analytics
  • Reporting and Communication Techniques
  • Quality Assurance and Improvement of Audit Process
  • Laws, Regulations, and Industry Standards
  • Organizational Structure, IT Governance, and IT Strategy
  • IT Policies, Standards, Procedures, and Guidelines
  • Enterprise Architecture and Considerations
  • Enterprise Risk Management (ERM)
  • Privacy Program and Principles
  • Data Governance and Classification
  • IT Resource Management
  • IT Vendor Management
  • IT Performance Monitoring and Reporting
  • Quality Assurance and Quality Management of IT
  • Project Governance and Management
  • Business Case and Feasibility Analysis
  • System Development Methodologies
  • Control Identification and Design
  • System Readiness and Implementation Testing
  • Implementation Configuration and Release Management
  • System Migration, Infrastructure Deployment, and Data Conversion
  • Postimplementation Review
  • IT Components
  • IT Asset Management
  • Job Scheduling and Production Process Automation
  • System Interfaces
  • End-user Computing and Shadow IT
  • Systems Availability and Capacity Management
  • Problem and Incident Management
  • IT Change, Configuration, and Patch Management
  • Operational Log Management
  • IT Service Level Management
  • Database Management
  • Business Impact Analysis
  • System and Operational Resilience
  • Data Backup, Storage, and Restoration
  • Business Continuity Plan
  • Disaster Recovery Plans
  • Information Asset Security Policies, Frameworks, Standards, and Guidelines
  • Physical and Environmental Controls
  • Identity and Access Management
  • Network and End-Point Security
  • Data Loss Prevention
  • Data Encryption
  • Public Key Infrastructure (PKI)
  • Cloud and Virtualized Environments
  • Mobile, Wireless, and Internet-of-Things Devices
  • Security Awareness Training and Programs
  • Information System Attack Methods and Techniques
  • Security Testing Tools and Techniques
  • Security Monitoring Logs, Tools, and Techniques
  • Security Incident Response Management
  • Evidence Collection and Forensics
Learning outcomes

What you'll learn

Reduce risk: CISAs provide assurance that the organization’s IT and business systems are effectively monitored, managed and protected.
Create a common language: CISAs serve as trusted business advisors by assuring that the necessary leadership and organizational structures and processes are in placed to achieve business objectives and support the enterprise’s strategy.
Drive business successes: Regulators and clients look for a CISA designation and many businesses and government agencies require it.

Skills you'll learn

8 skills
IT Audit Planning
Audit Risk Assessment
IT Governance
Audit Testing
Information Security Auditing
IT Compliance
IT Audit Reporting
IT Audit Quality Assurance

Certificate

·       Attendance Certificate from CLS Learning Solutions

·       This course enables you to pass Certified Information Systems Auditor CISA Exam
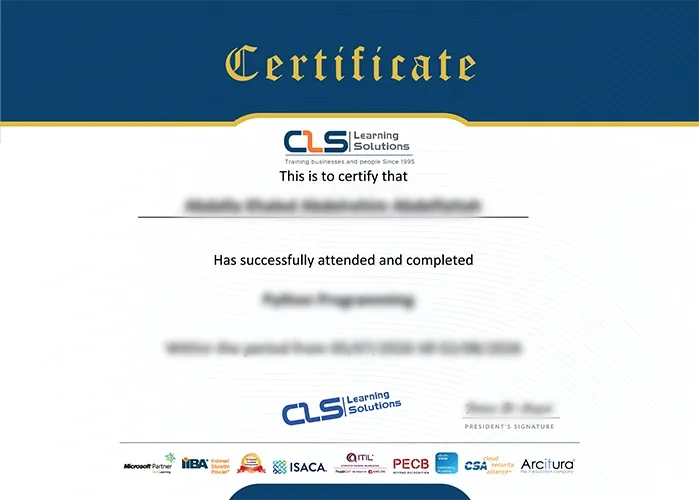

Certified Information Systems Auditor CISA

Potential Career Paths

IT Audit Directors
IT Managers
Compliance/Risk Directors
Information Systems Auditor
IT Governance Specialist
GRC Analyst